Norm Secure
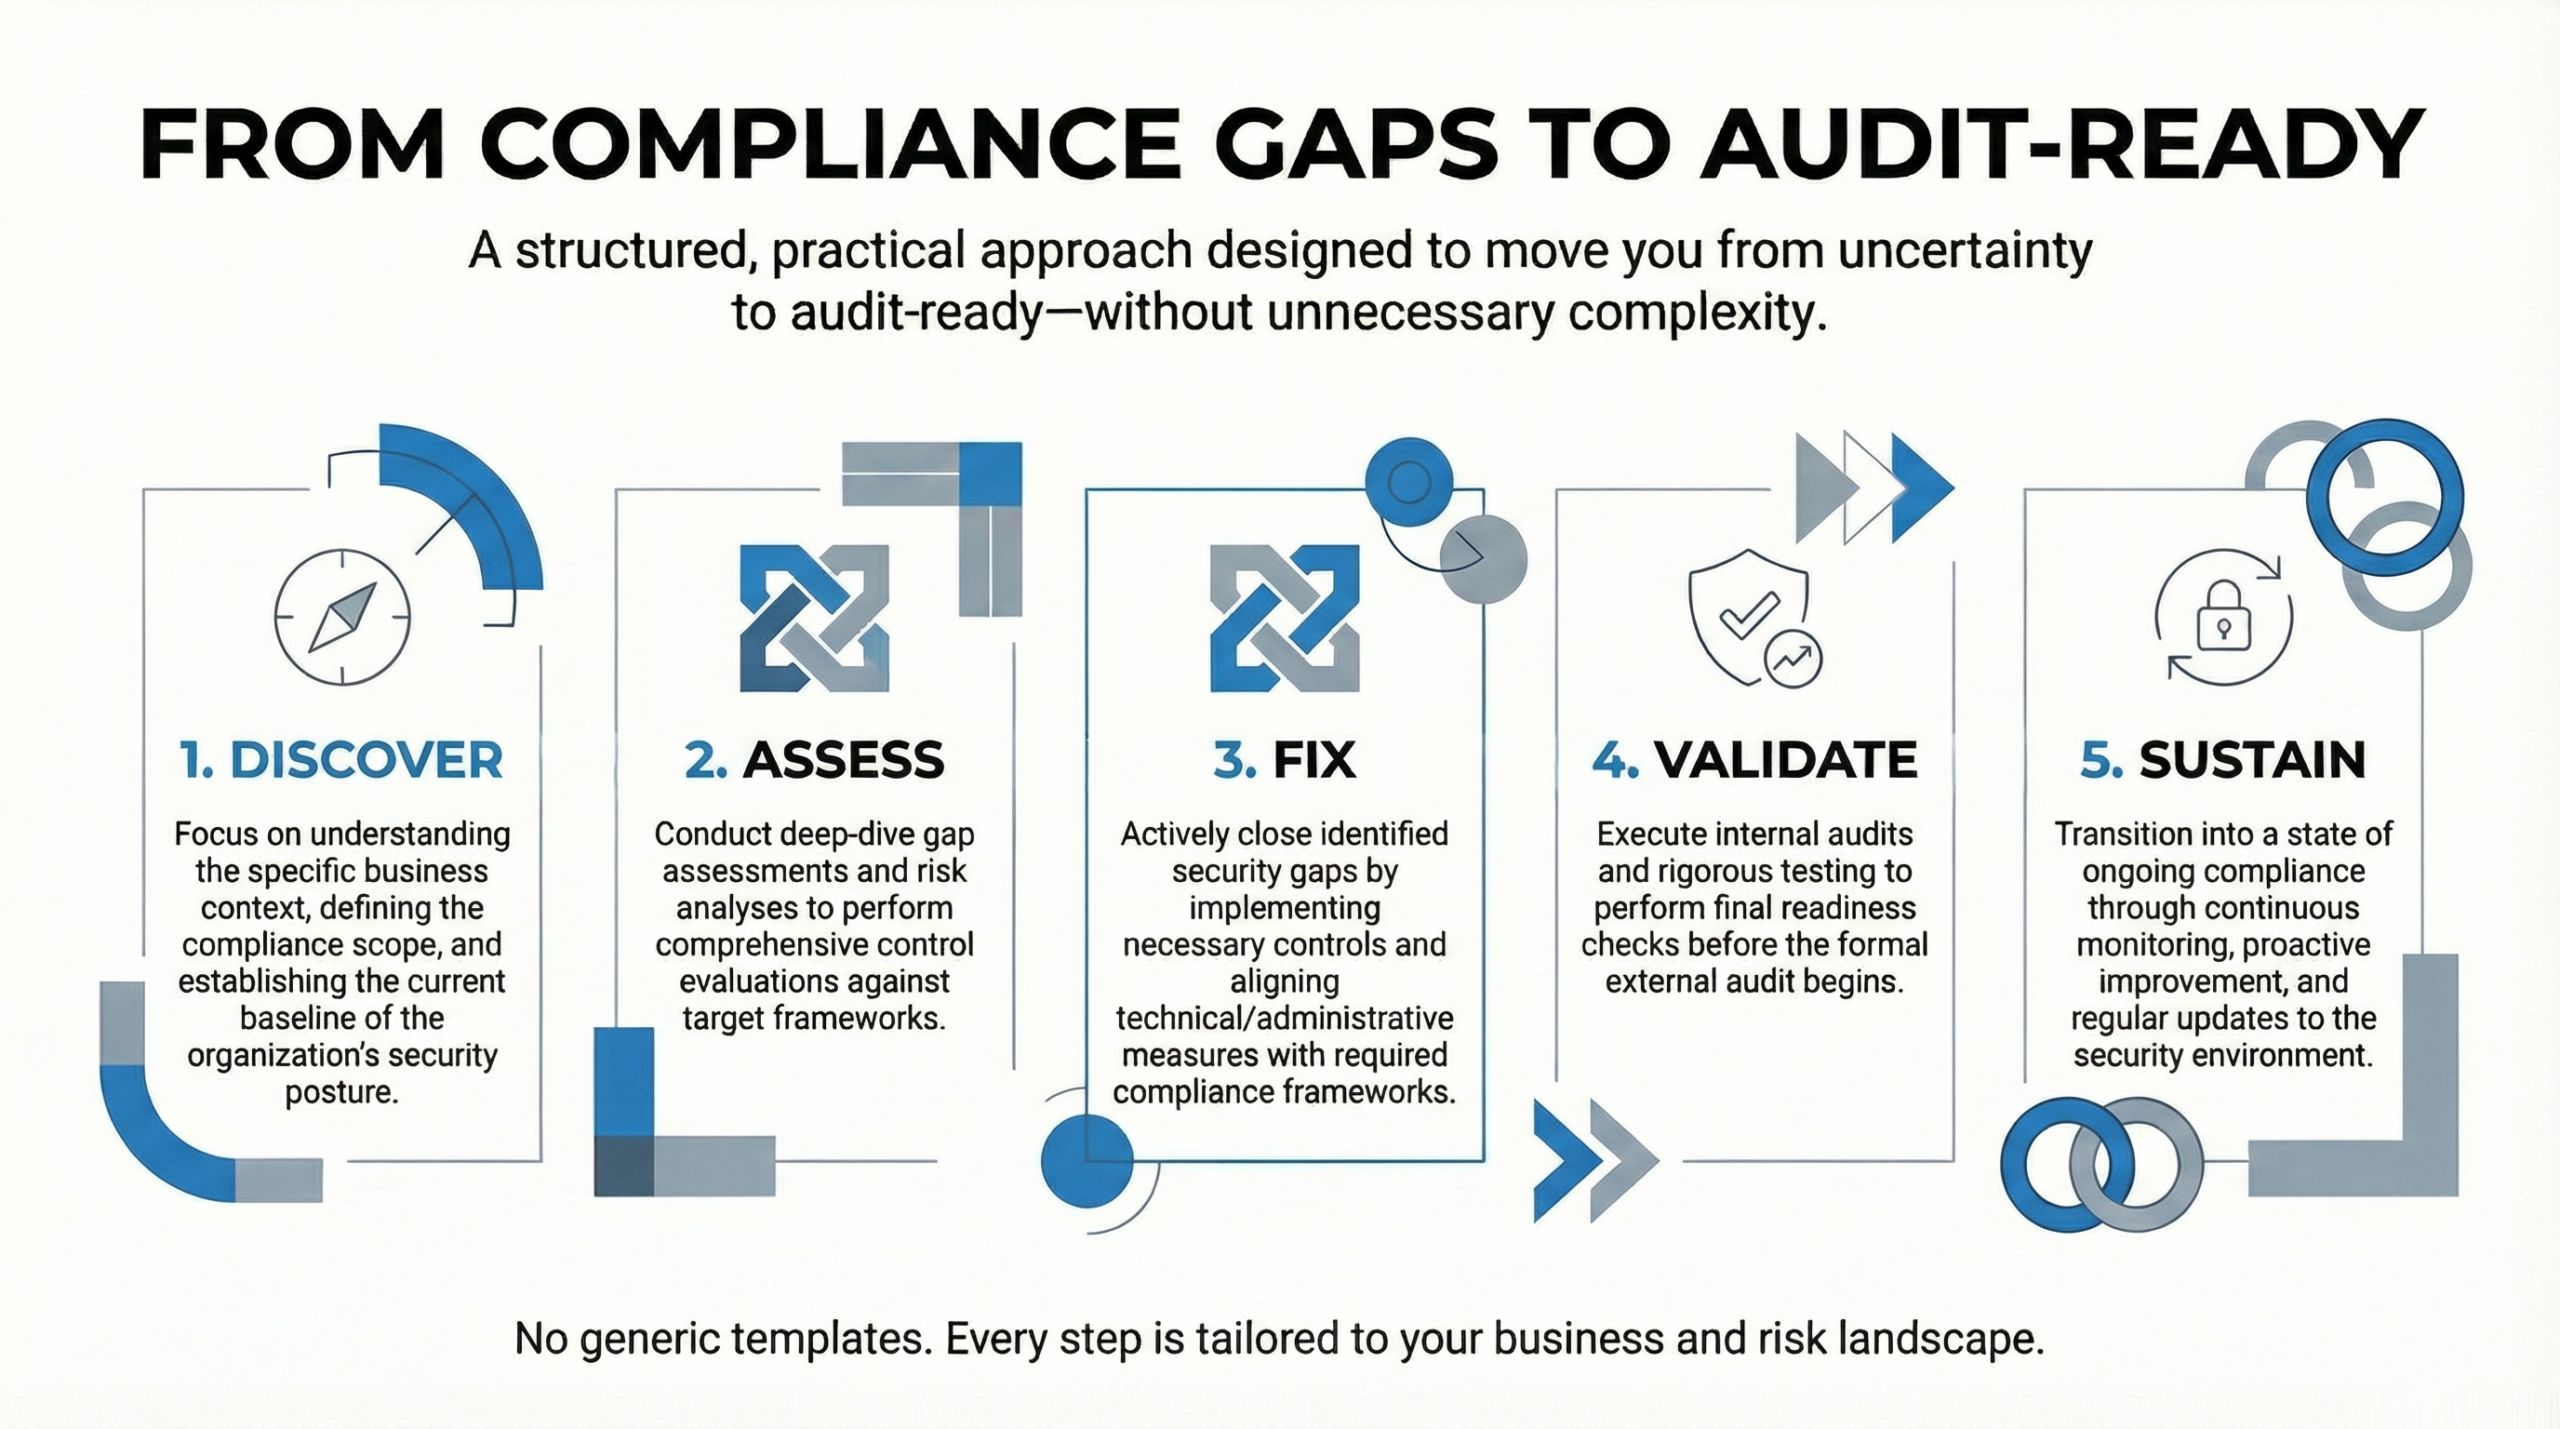
Fix Compliance Gaps. Reduce Risk. Build Trust. From identifying gaps to achieving audit readiness—we help you build security and compliance programs that are practical, scalable, and built for real-world execution.
Traditional Compliance Assessment NormSecure DPDP Assessment Weeks of manual reviews 20–30 minute guided assessment Expensive consulting engagement Affordable fixed-price assessment Generic checklists 70+ expert-designed compliance checks Limited visibility Executive readiness score & risk analysis Unclear next steps Prioritized recommendations & roadmap
Empowering Success Together
Its Time to Stand Apart Answer a structured questionnaire, receive an instant readiness score, identify compliance gaps, and download a professional executive report with prioritized recommendations.
Will You Pass Your ISO 27001 Audit?
Get a quick, real-world assessment of your security posture and identify gaps before the auditor does.
End-to-End Security, Risk & Compliance From assessment to implementation—we don’t just advise, we execute.
Compliance & Certification Readiness Prepare for audits with confidence—covering ISO, SOC, privacy laws, and other regulatory requirements.
Risk & Gap Assessments
Audit & Assurance Internal audits, control testing, and pre-certification reviews to ensure you’re truly audit-ready.
Security Program Implementation Build and enhance ISMS, policies, governance structures, and incident response capabilities.
Specialized Training Programs Built for teams that need to implement—not just understand—security and compliance
01.
ISO 27001 Practitioner Bootcamp Hands-on training covering ISMS design, risk assessment, and certification readiness.
02.
SOC 2 Readiness Workshop Practical sessions focused on control mapping, evidence preparation, and audit expectations.
03.
GRC Framework Design Training Build governance structures, risk models, and control frameworks aligned with business operations.
04.
BCMS & BIA Practitioner Training Develop business continuity plans, impact analysis, and resilience strategies.
05.
AIMS ISO 42001 Governance Implementation Understand AI risks, governance models, and compliance requirements aligned with ISO 42001.
06.
AI Risk & Governance Strategy Design and implement AI governance frameworks aligned with business, risk, and regulatory expectations.
Available as customized, organization-specific workshops.
Not Sure Where You Stand? Most organizations fail audits due to gaps they didn’t know existed.
Take our quick assessment to: – Identify high-risk areas
What Sets Us Apart? Built on real-world experience—not just frameworks and theory.
Ground Reality Driven Not theory or templates—real-world security leadership applied to your environment.
Audit-Ready Means Evidence-Ready We prepare you for real audits—with clear evidence, not just documentation.
Built for Speed Without Breaking Compliance Move fast, fix gaps, and get audit-ready—without slowing down your business.
We Close Gaps. Not Just Report Them Most consultants stop at findings. We stay until controls are implemented and working.
One Partner. All Frameworks ISO, SOC 2, DPDP, HIPAA or beyond—we align everything into one cohesive program.
We Think Like Auditors Before They Arrive So there are no surprises during certification or client audits.
Designed for organizations that want results—not reports.
Don’t Let Your Next Audit Be a Surprise We help you identify gaps early, fix them fast, and walk into audits with confidence.
Audit-ready in weeks, not months.